NetDoctor
Offline Cisco diagnostics that show their evidence.
Play with it, right here.
A working demo with sample data. Nothing here touches a real system.
- Collect1 config · 72 lines
- Parse8 interfaces · 4 VLANs
- Normalise1 snapshot
- Evaluate122 checks
- Present5 findings
Pipeline: Done · 5 findings · 117 checks passed
! acc-sw3 · running-config · sample version 17.9 service timestamps log datetime msec localtime service password-encryption hostname acc-sw3 ! clock timezone EET 2 0 ip domain name site-a.example ! vlan 10 name USERS vlan 20 name PRINTERS vlan 30 name VOICE vlan 99 name MGMT ! spanning-tree mode rapid-pvst spanning-tree extend system-id ! interface Port-channel1 description UPLINK core-sw1 Po11 switchport mode trunk switchport trunk allowed vlan 10,20,99 ! interface GigabitEthernet1/0/1 description DESK 2.14 switchport mode access switchport access vlan 10 switchport voice vlan 30 spanning-tree portfast ! interface GigabitEthernet1/0/7 switchport mode access switchport access vlan 10 switchport voice vlan 30 spanning-tree portfast ! interface GigabitEthernet1/0/12 description MEETING ROOM 2 switchport mode access switchport access vlan 10 spanning-tree portfast spanning-tree bpduguard enable ! interface GigabitEthernet1/0/24 description AP-2F-EAST switchport mode access switchport access vlan 99 spanning-tree portfast ! interface GigabitEthernet1/0/49 description UPLINK core-sw1 Gi1/0/3 channel-group 1 mode active ! interface GigabitEthernet1/0/50 description UPLINK core-sw1 Gi2/0/3 channel-group 1 mode active ! interface Vlan99 ip address 10.99.0.13 255.255.255.0 ! ip default-gateway 10.99.0.1 logging host 10.99.0.20 ntp server ‹site NTP›expected, not foundsnmp-server community <removed> RO ! line vty 0 4 login local transport input telnet ssh ! end 117 checks passed
Pick a finding to see its evidence.
Gi1/0/12 err-disabled by BPDU guard
- Rule
- STP-012 · BPDU guard tripped
- Baseline
Edge ports may trip BPDU guard, with err-disable recovery configured- Observed
Gi1/0/12 err-disabled (bpduguard) since 09:41 · no recovery configured- Evidence
- acc-sw3.cfg, line 45
Why it matters. Someone plugged a switch or a looped cable into Meeting room 2. BPDU guard shut the port to protect the network, so the room stays offline until somebody re-enables it.
Next step. Find and unplug what is on Gi1/0/12, then bounce the port. Consider errdisable recovery for bpduguard. NetDoctor only suggests; it never changes a device.
VLAN 30 missing on uplink trunk Po1
- Rule
- L2-TRUNK-004 · VLAN in use but not carried
- Baseline
Every VLAN used on an access port is allowed on the uplink- Observed
VLAN 30 (VOICE) used on 2 ports · Po1 allows 10, 20, 99- Evidence
- acc-sw3.cfg, line 25
Why it matters. Desk phones on this switch get power and a link, but their traffic never leaves the switch: no dial tone.
Next step. Add VLAN 30 to the allowed list on Po1, and check the same trunk on core-sw1. NetDoctor only suggests; it never changes a device.
Remote access allows Telnet
- Rule
- SEC-MGMT-002 · Clear-text management
- Baseline
transport input ssh- Observed
transport input telnet ssh on vty 0 4- Evidence
- acc-sw3.cfg, line 70
Why it matters. Telnet sends usernames and passwords in clear text, so anyone on the path can read them.
Next step. Allow SSH only on the vty lines. NetDoctor only suggests; it never changes a device.
Gi1/0/7 has no description
- Rule
- DOC-001 · Undocumented access port
- Baseline
Every port in use has a description- Observed
Gi1/0/7 up/up · no description line- Evidence
- acc-sw3.cfg, line 34
Why it matters. When it breaks at 3 a.m., nobody knows what is plugged in there or who to call.
Next step. Describe the port after its desk or device, like the other ports. NetDoctor only suggests; it never changes a device.
No NTP server configured
- Rule
- TIME-001 · Time source
- Baseline
At least one ntp server- Observed
No "ntp server" line in 72 lines- Evidence
- acc-sw3.cfg, missing after line 65
Why it matters. The clock drifts, so this switch's logs cannot be lined up with the rest of the network during an incident.
Next step. Point the switch at the site's NTP servers. NetDoctor only suggests; it never changes a device.
Select a device to see how it was discovered.
net-doctor.vercel.app, as it is today.
The real website. Switch between desktop and phone, then open it for the full experience.
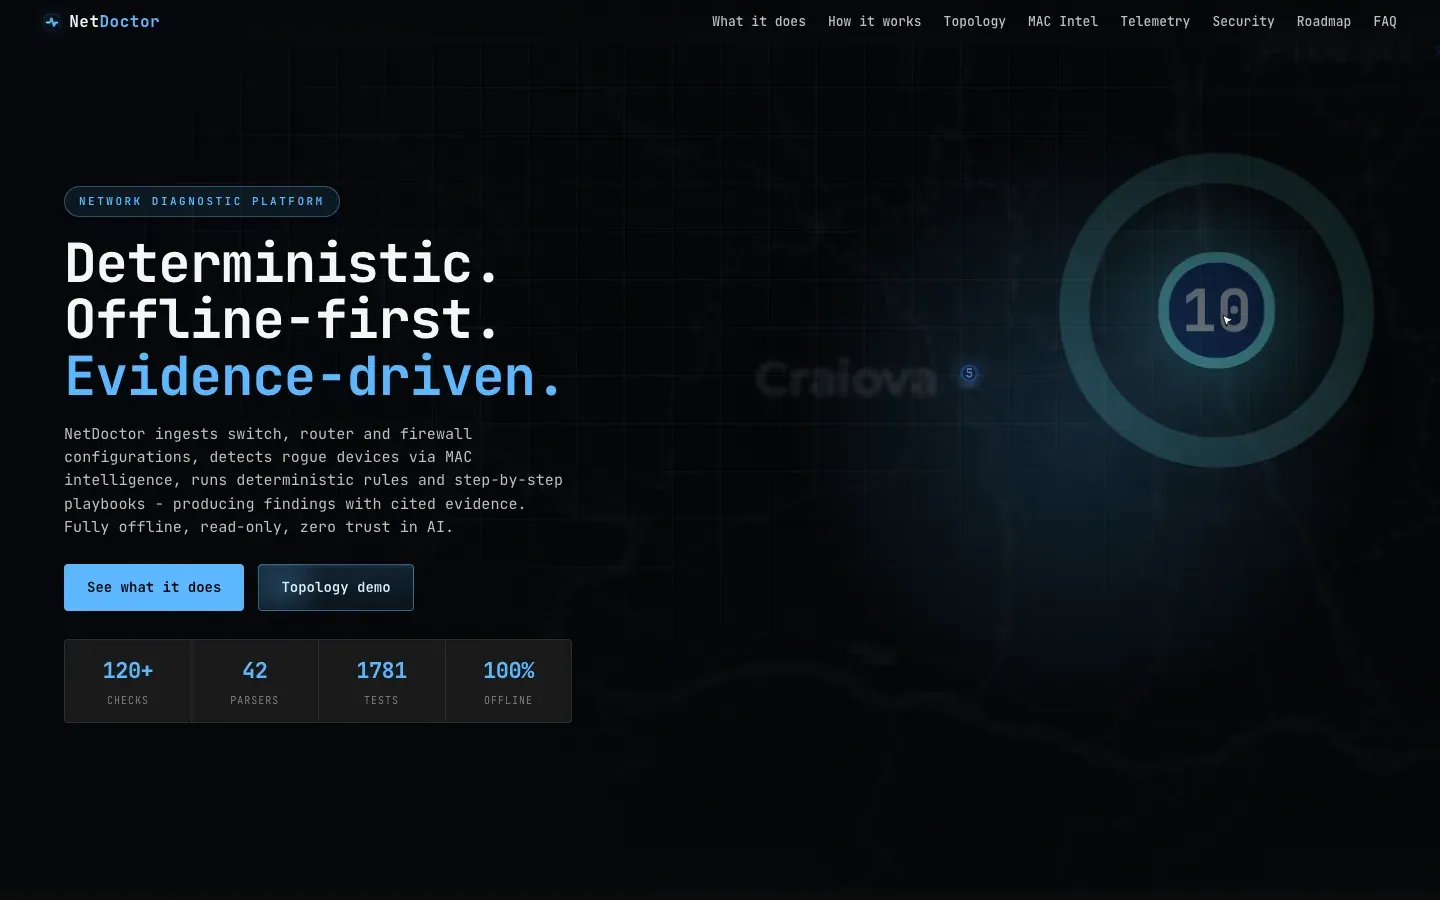
Overview
- Role
- Creator
- Year
- 2025
- Platforms
- Web · local
- Status
- Live
NetDoctor reads switch and firewall configurations, spots rogue devices from MAC data and runs deterministic checks and step-by-step playbooks. Every finding comes with its evidence. It works fully offline and never changes a device.
A five-stage pipeline collects the configs, or pulls them over read-only SSH, parses them with 42 dedicated Cisco IOS and IOS-XE parsers, builds one clean snapshot that separates what is configured from what is observed, checks it against a layered baseline, and shows the results as dashboards and topology maps.
Every finding is traceable: which file, which line, which value, which rule. The same input always gives the same output. An optional local model can explain a finding in plain words, but it is never the source of truth, and no data leaves the machine.
Safety is built in: no arbitrary commands and no write access. Secrets are stripped before any export, stored credentials are encrypted, and 689 tests keep the parsers and rules honest.
7 things it does well.
- 42 Cisco IOS and IOS-XE parsers
- 120+ deterministic checks, each citing its evidence
- Read-only SSH collection
- Site topology from CDP and LLDP
- Offline MAC intelligence: vendor lookup, flapping and rogue devices
- Encrypted credential vault, roles and scheduled backups
- 689 automated tests
Built with
- Python
- Next.js
- TypeScript
- PostgreSQL
- Cisco IOS
- Scrapli